HackersRange Academy

Learn cyber by doing the real work.

One clear path from zero experience to a job-ready security specialist, offensive or defensive. Every course runs on a live company network where you work through real attacks, so by the day you finish, you have already done the job.

Academy credentials, HackersRange Certified
HRCF HRCSA HRCIR HRCPT HRCRTO
How the academy works

Learn it. Prove it on the range.

Every track is delivered the same way: instruction frames the discipline, then the majority of your hours are spent operating a live, instrumented enterprise, assessed on evidence, not multiple choice.

Start at the foundation

Intro to Cyber builds the computing, networking, Linux and Windows base every specialist track assumes.

Choose a career branch

Move into offensive (Penetration Testing) or defensive (SOC, IR/DFIR) work, or add a cloud and OT specialization.

Work the live range

Browser-reachable, fully isolated environments with real adversary activity replayed in, both sides fully instrumented.

Earn the credential

Each track closes with a graded capstone and an HRC certification mapped to the role you are training for.

We practice what we preach

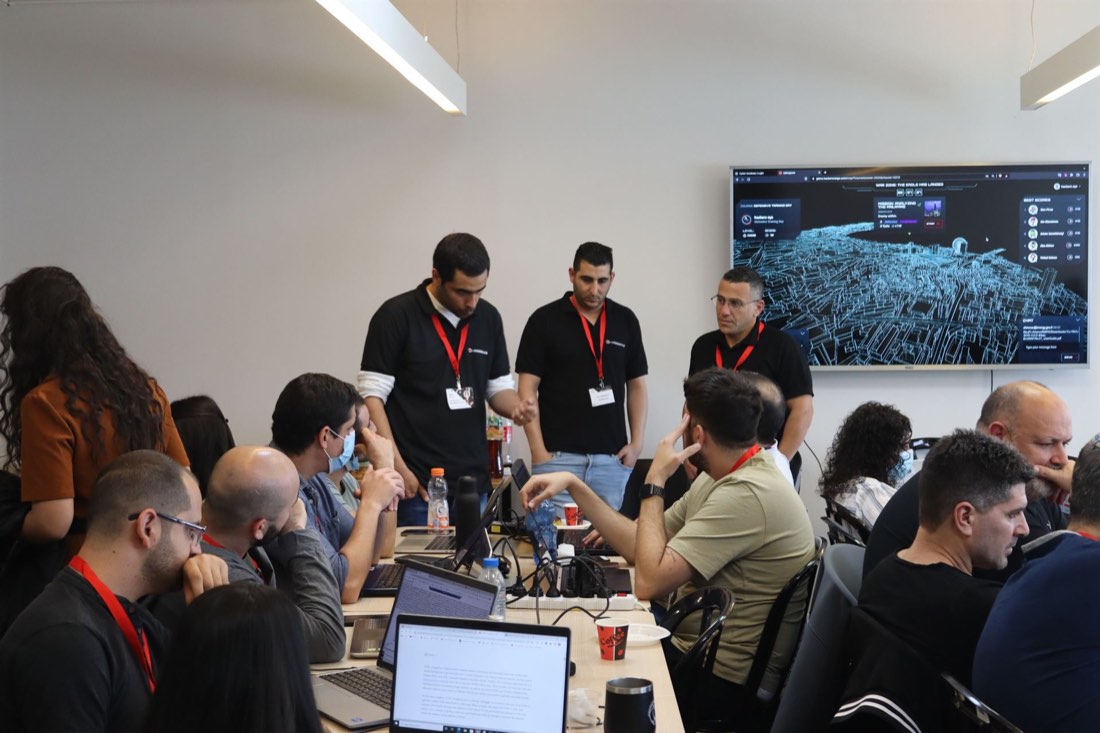
Taught by the operators who run the real engagements.

HackersEye is a working offensive and incident-response firm. The same red teamers, penetration testers, DFIR analysts and SOC operators who break into and defend live enterprises write the syllabus and teach the range, so what you learn is current tradecraft drawn from real attacks, not theory rewritten from a textbook.

Every module is reverse-engineered from work we actually do in the field, then rebuilt as something you can attack and defend on the range.

HackersEye, Offensive · IR · SOC
The learning path

One foundation. Two career branches.

The HackersRange ladder starts with a single mandatory on-ramp, rises into offensive and defensive specialist tracks, and tops out in advanced red team operations and DFIR, with cloud and OT specializations alongside.

Foundation (required) Defensive tracks Offensive tracks Specializations
Tracks & curriculum

What you actually learn and build.

Real modules, real hours and real outcomes from the HackersRange syllabus. Each track closes with a graded capstone on the range and an HRC credential.

Computing & Operating System Fundamentals12 hours

You learn how a computer really works underneath, files, processes, memory and user accounts, by driving a live machine yourself. This gives you the mental model every security task later depends on.

  • OS internals
  • File systems
  • Process basics
Networking Essentials15 hours

You follow real traffic across a small network and see how data actually moves between machines, ports and services. By the end you can read an IP address, a port and a packet and say what is happening.

  • TCP/IP basics
  • Ports & services
  • Packet reading
Linux for Security16 hours

You work entirely from the Linux command line to move files, manage permissions and automate tasks with short Bash scripts. This is the daily working environment for almost every security tool you will meet.

  • Linux CLI
  • Bash scripting
  • Permissions
Windows for Security16 hours

You drive Windows the way a professional does, through PowerShell, the registry and the event logs rather than the desktop. You learn where Windows records what happened, which matters for both attack and defence.

  • PowerShell
  • Windows internals
  • Event logs
Security Fundamentals & the Threat Landscape14 hours

You learn the core ideas of security, risk, controls and how real attacks unfold, using plain language and current examples. This gives you the vocabulary to talk about threats with any team.

  • Security concepts
  • Threat landscape
  • Risk basics
Web & Application Basics14 hours

You take apart how websites and applications work by inspecting requests and responses with Burp Suite. You see where common weaknesses live before you ever try to exploit or defend one.

  • HTTP basics
  • Web requests
  • App structure
Offensive vs Defensive Foundations15 hours

You watch the same event from both sides, the attacker's action and the defender's trace of it, on the live range. This shows you why offensive and defensive work are two views of one story.

  • Attacker mindset
  • Defender view
  • Kill chain
Tooling, Lab Discipline & Documentation18 hours

You set up a clean working lab and complete a guided two-sided intrusion, recording every step as you go. The graded capstone scores how well you work and document, not what you memorised.

  • Lab setup
  • Note-taking
  • Guided intrusion

You will graduate able to

  • Reason about security at the OS, file-system, process and network level.
  • Operate confidently on the Linux and Windows command lines and script in Bash and PowerShell.
  • Capture and interpret network traffic, and complete a guided two-sided intrusion on a live range.

Tools & certification path

WiresharkKali LinuxPowerShellBashBurp SuiteVirtualBox
  • Aligns to CompTIA Security+, Network+ and ISC2 CC.
SOC Operations & Frameworks12 hours

You learn how a security operations centre is run day to day and how work flows from alert to action. You map that work to the frameworks a real team uses so you fit in from day one.

  • SOC workflow
  • MITRE ATT&CK
  • Analyst tiers
Log Sources & Telemetry14 hours

You collect logs from Windows, Linux, network and cloud systems and learn what each one can and cannot tell you. This teaches you where to look before an alert ever fires.

  • Log sources
  • Telemetry
  • Data mapping
SIEM Fundamentals, Splunk & Elastic Security18 hours

You load real data into Splunk and the Elastic Stack and write your own searches to find suspicious activity. This is the core console you will live in as an analyst.

  • Splunk search
  • Elastic queries
  • Dashboards
Network Security Monitoring16 hours

You inspect live network traffic with Zeek and Suricata to spot scanning, beacons and data leaving the estate. You learn to separate normal chatter from a real intrusion.

  • Zeek
  • Suricata
  • Traffic analysis
Endpoint Detection & Response17 hours

You use an EDR and Sysmon data to watch what programs actually do on a machine and catch malicious behaviour. You investigate a compromised host from the endpoint outward.

  • EDR
  • Sysmon
  • Endpoint triage
Detection Engineering18 hours

You write detections as code, Sigma and Elastic rules, then test and tune them against real attacks on the range. You learn to cut false alarms without missing the real thing.

  • Sigma rules
  • Detection tuning
  • Rule testing
Alert Triage & Investigation18 hours

You take a queue of live alerts and decide quickly which are real, which are noise and which need to escalate. You build the evidence trail that supports each decision.

  • Alert triage
  • Investigation
  • Escalation
Cyber Threat Intelligence for the SOC15 hours

You enrich alerts with threat intelligence in MISP and learn which indicators are worth acting on. This turns a raw alert into a picture of who might be attacking and why.

  • Threat intel
  • MISP
  • IOC enrichment
Threat Hunting Fundamentals17 hours

You form a hypothesis about how an attacker might be hiding and go looking for them before any alert fires. Your hunts are mapped to MITRE ATT&CK so the results are repeatable.

  • Threat hunting
  • Hypotheses
  • ATT&CK mapping
Incident Handling for Analysts16 hours

You run a live incident through its early stages and learn a clean handoff to the incident response team. You practise keeping calm records while an attack is still unfolding.

  • Incident handling
  • IR handoff
  • Containment basics
SOAR & Automation15 hours

You build simple automated playbooks so repetitive tasks handle themselves and analysts focus on real judgement. You see how automation speeds response without removing the human decision.

  • SOAR
  • Playbooks
  • Automation
Reporting, Metrics & Communication24 hours

You write clear incident write-ups and track the metrics that show whether the SOC is working. The graded capstone scores a full monitor-triage-hunt run on the live range.

  • Reporting
  • SOC metrics
  • Communication

You will graduate able to

  • Operate a SIEM and an EDR to monitor and investigate an enterprise estate.
  • Write, test and tune detections as code, including Sigma and Elastic rules.
  • Run hypothesis-driven threat hunts mapped to MITRE ATT&CK and hand off to IR.

Tools & certification path

SplunkElasticsearchKibanaSysmonZeekSuricataMISP
  • Aligns to BTL1, CompTIA CySA+ and Microsoft SC-200.
Incident Response Lifecycle & Governance16 hours

You learn the full incident lifecycle from preparation to lessons learned, and the roles and decisions at each stage. This gives you the plan you follow when a real breach lands.

  • IR lifecycle
  • Governance
  • Playbooks
Evidence Acquisition & Forensic Soundness20 hours

You capture disks and data in a way that holds up later, with an unbroken chain of custody. You learn why how you collect evidence matters as much as what you find.

  • Evidence capture
  • Chain of custody
  • Imaging
Windows Forensics I, File System & Registry22 hours

You dig into the Windows file system and registry to see what was installed, run and changed. You reconstruct attacker footprints from the traces Windows leaves behind.

  • NTFS artifacts
  • Registry analysis
  • RegRipper
Windows Forensics II, Logs, Execution & Timeline24 hours

You pull execution evidence and event logs together into one timeline of what happened and when. You use Plaso to build a defensible sequence of the attack.

  • Event logs
  • Execution artifacts
  • Timelining
Memory Forensics24 hours

You capture and analyse system memory with Volatility 3 and MemProcFS to find malware that never touched the disk. Memory often holds the clearest picture of a live intrusion.

  • Volatility 3
  • MemProcFS
  • Memory analysis
Linux & Cloud Forensics24 hours

You investigate compromised Linux hosts and cloud accounts, including the Microsoft 365 audit log. You learn where the evidence lives when the crime scene is a server or a tenant.

  • Linux forensics
  • Cloud logs
  • M365 UAL
Network Forensics22 hours

You reconstruct an attack from captured network traffic, tracing command channels and stolen data. You learn to prove what left the network even when the host is wiped.

  • PCAP analysis
  • C2 tracing
  • Exfil detection
Malware Triage & Behavioral Analysis24 hours

You safely detonate and observe a suspicious file to learn what it does without full reverse engineering. You extract the indicators the rest of the team needs to hunt with.

  • Malware triage
  • Behavioral analysis
  • IOC extraction
Email Compromise & BEC Investigations22 hours

You investigate a hijacked mailbox and a business email fraud, following logins, rules and message paths. You learn how these common, costly attacks actually play out.

  • BEC investigation
  • Mailbox forensics
  • Header analysis
Cyber Threat Intelligence & Attribution22 hours

You tie the evidence to known attacker groups and techniques and judge how confident that link really is. You learn to attribute carefully without overreaching.

  • Attribution
  • TTP mapping
  • Intel analysis
Containment, Eradication & Recovery24 hours

You cut off an active attacker, remove their access and restore the business safely without losing evidence. You practise the hard calls made under pressure during a real breach.

  • Containment
  • Eradication
  • Recovery
DFIR Reporting & Expert Communication36 hours

You turn your investigation into a defensible report and a clear executive briefing. The graded capstone scores a full incident run end to end on genuinely compromised range systems.

  • DFIR reporting
  • Executive briefing
  • Timeline defence

You will graduate able to

  • Acquire evidence in a forensically sound manner with a defensible chain of custody.
  • Perform Windows, Linux, cloud, memory and network forensics to reconstruct attacker activity.
  • Reconstruct a defensible timeline and produce DFIR reporting and executive briefings.

Tools & certification path

KAPEAutopsyVolatility 3MemProcFSPlasoRegRipperM365 UAL
  • Aligns to GIAC GCFA, GCFE, GCIH and GREM (partial).
Methodology, Scoping & Ethics12 hours

You learn how a real engagement is scoped, agreed and kept inside legal and ethical limits. This is the professional discipline that separates a tester from an attacker.

  • Scoping
  • Ethics
  • Methodology
Reconnaissance & OSINT15 hours

You gather everything a target reveals about itself in public before you touch a single system. You build the map of people, domains and services that guides the whole test.

  • OSINT
  • Recon
  • Footprinting
Scanning & Enumeration16 hours

You use Nmap and related tools to find live hosts, open ports and running services across the range. You turn a raw network into a clear list of things worth attacking.

  • Nmap
  • Service enum
  • Port scanning
Vulnerability Analysis16 hours

You match the services you found to known weaknesses and judge which are real and which are noise. You learn to prioritise by impact, not by scanner score.

  • Vuln analysis
  • Prioritisation
  • Verification
Exploitation Fundamentals18 hours

You get your first real foothold, using Metasploit and manual techniques to turn a weakness into access. You learn what a working exploit actually looks like on a live host.

  • Exploitation
  • Metasploit
  • Foothold
Web Application Pentesting I18 hours

You attack web applications with Burp Suite, exploiting injection, broken access and authentication flaws. You learn the OWASP-style weaknesses that dominate real reports.

  • Web attacks
  • Burp Suite
  • Injection
Web Application Pentesting II18 hours

You take on harder web targets, chained bugs, tricky logic flaws and modern app defences. You learn to think past the obvious and combine weaknesses into a real breach.

  • Advanced web
  • Bug chaining
  • Logic flaws
Password & Credential Attacks16 hours

You capture and crack credentials with Hashcat and learn how stolen passwords open the next door. You see why weak and reused passwords are still the fastest way in.

  • Hashcat
  • Cred attacks
  • Password cracking
Active Directory Fundamentals18 hours

You learn how Windows Active Directory really works, users, groups, trusts and where it is weak. This is the backbone of almost every enterprise you will ever test.

  • Active Directory
  • Kerberos
  • AD structure
Active Directory Attacks20 hours

You map an AD domain with BloodHound and Impacket and follow the paths that lead to full control. You learn the attacks that take a tester from one user to domain admin.

  • BloodHound
  • Impacket
  • AD attacks
Privilege Escalation17 hours

You turn a low-privilege foothold into full control on both Windows and Linux hosts. You learn to spot the misconfigurations that hand you the keys.

  • Privesc
  • Windows & Linux
  • Misconfig hunting
Post-Exploitation & Pivoting18 hours

You use one compromised host to reach deeper into the network and pivot toward hidden systems. You learn how attackers spread from a single foothold to the whole estate.

  • Post-exploitation
  • Pivoting
  • Lateral movement
Reporting & Remediation38 hours

You write a clear, professional report that a client can actually act on, with practical fixes. The graded capstone scores a full external-to-domain-compromise assessment on the range.

  • Pentest reporting
  • Remediation
  • Client comms

You will graduate able to

  • Scope an engagement and operate within legal and ethical constraints.
  • Exploit network, web-application and Active Directory weaknesses to escalate access.
  • Move from external foothold to domain compromise and write a professional report.

Tools & certification path

NmapBurp SuiteMetasploitBloodHoundImpacketHashcatCrackMapExec
  • Aligns to OffSec OSCP, TCM PNPT, INE eJPT/eCPPT and PenTest+.
Red Team Operations & Adversary Emulation24 hours

You plan a full red team engagement that copies how a chosen real-world attacker behaves. You learn to run an operation with clear goals, rules and OPSEC rather than just breaking in.

  • Red team ops
  • Adversary emulation
  • OPSEC
Advanced Active Directory Attacks28 hours

You attack hardened and multi-domain Active Directory setups that the basic techniques no longer beat. You learn the trust and delegation abuses that lead to cross-forest control.

  • Advanced AD
  • Trust abuse
  • Delegation
Advanced Kerberos & Ticket Attacks28 hours

You forge and abuse Kerberos tickets with Rubeus and Mimikatz to move and persist unseen. You learn the ticket attacks that quietly grant lasting access to a domain.

  • Kerberos attacks
  • Rubeus
  • Ticket forging
Evasion & Defense Bypass30 hours

You rework your tools and techniques to slip past production EDR and logging. You learn what actually triggers a defender and how modern operators stay quiet.

  • EDR evasion
  • Defense bypass
  • Obfuscation
Command & Control Infrastructure28 hours

You stand up resilient C2 with Cobalt Strike, Sliver and Mythic and shape traffic to blend in. You learn to run and hide the channel that controls your implants.

  • C2 infrastructure
  • Cobalt Strike
  • Redirectors
Initial Access & Social Engineering Operations28 hours

You engineer a realistic way in, phishing, pretext and payloads that survive email and endpoint defences. You learn how modern intrusions actually start with a person, not a port.

  • Initial access
  • Phishing
  • Payload delivery
Advanced Web & API Exploitation28 hours

You break modern web applications and APIs, chaining deep flaws to reach internal systems. You learn the server-side and logic attacks that a standard test misses.

  • Advanced web
  • API exploitation
  • SSRF & chains
Exploit Development Fundamentals28 hours

You debug binaries with x64dbg and build a working exploit from a crash to code execution. You learn how memory-corruption bugs become the exploits that others just run.

  • Exploit dev
  • x64dbg
  • Memory corruption
Cloud & Hybrid Identity Attacks26 hours

You attack cloud tenants and the identity that links them to on-premises Active Directory with Certipy. You learn how attackers pivot between the network and the cloud.

  • Cloud attacks
  • Hybrid identity
  • Certipy
Lateral Movement, Persistence & Domain Dominance28 hours

You spread across a defended estate, plant durable persistence and take full domain control. You learn to hold access quietly while a live team hunts for you.

  • Lateral movement
  • Persistence
  • Domain dominance
Red Team Reporting & Purple Teaming44 hours

You turn the operation into a report defenders can act on and run a purple-team debrief with them. The graded capstone scores a full-scope engagement against a live monitoring team.

  • Red team reporting
  • Purple teaming
  • Debrief

You will graduate able to

  • Plan and run a full-scope red team engagement with adversary emulation and OPSEC.
  • Evade and operate against EDR and a live monitoring team using current tradecraft.
  • Achieve cross-forest domain dominance and deliver red and purple-team reporting.

Tools & certification path

Cobalt StrikeSliverMythicCertipyRubeusMimikatzx64dbg
  • Aligns to OffSec OSEP, Zero-Point CRTO, OSWE and Altered Security CRTP/CRTE.
Inside the platform

Every hour is spent on the range.

The academy is taught entirely on HackersRange, browser-reachable, fully isolated environments where you work real attacks and your progress is tracked, assessed and certified inside one console.

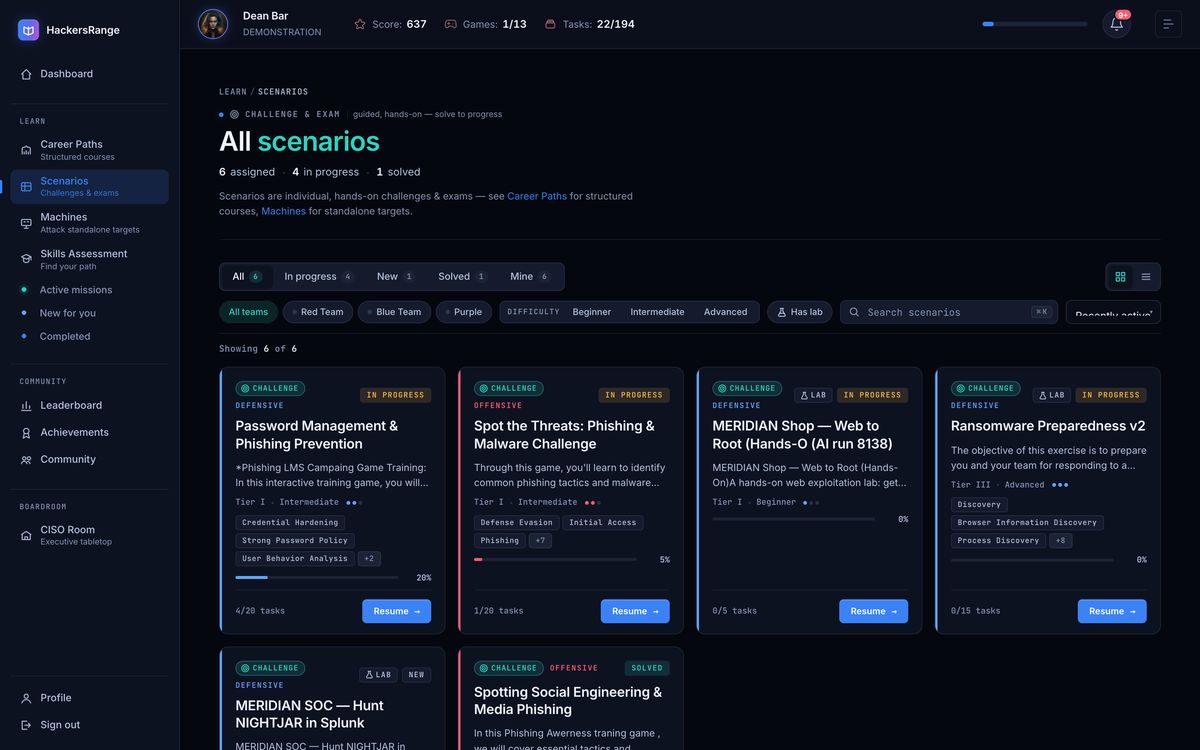
HackersRange — your scenarios in progress, resume where you left off

Your learning command centre

One workspace ties your track, scheduled labs, your own always-on range and progress together, pick up exactly where you left off, on any machine.

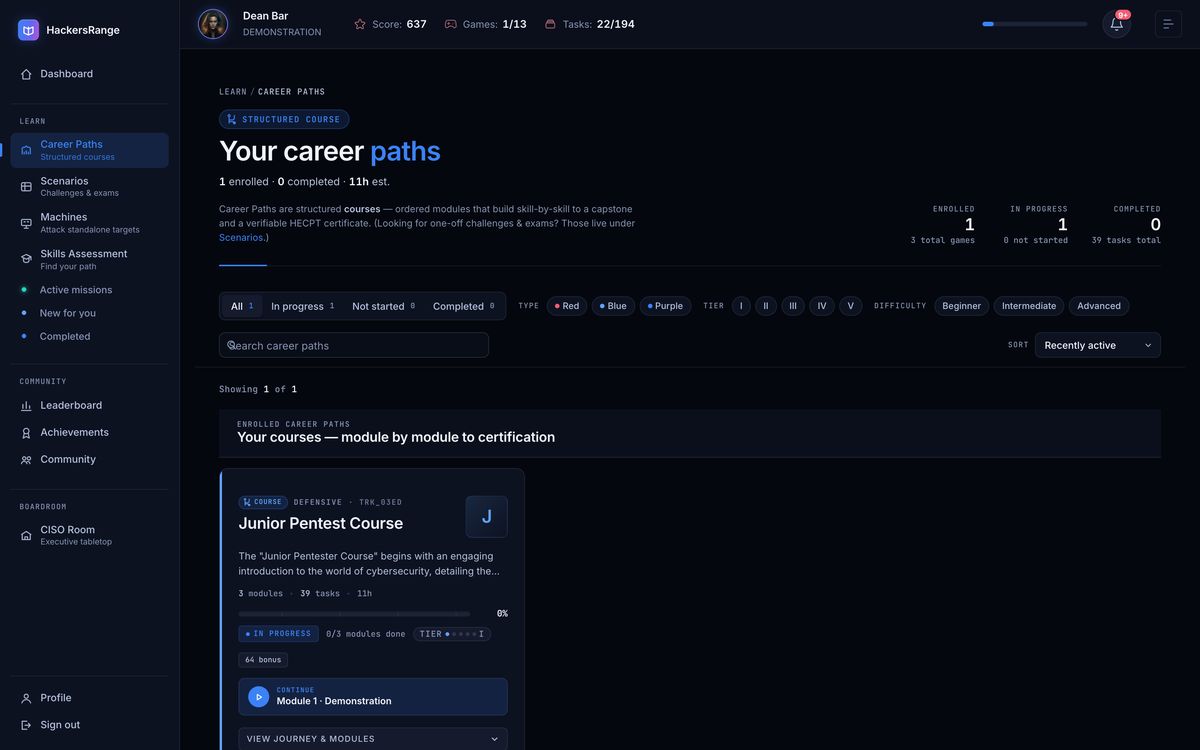
HackersRange — career-path courses, module by module to an HRC certification

Courses & certifications

Modules, hands-on labs and graded capstones are organised by track, with HRC credentials issued on evidence of work completed on the range.

The range captures host, network and cloud telemetry in full. Offensive learners watch what their actions leave behind; defensive learners work from the same complete record a real analyst would have. Instructors observe every environment from a console and can step in inside the same session.

Explore the range
Why train on a live range

A real enterprise, not a simplified lab.

Each track runs on a managed, fully isolated range that recreates a real estate, Windows AD, production-grade EDR, network sensors, a SIEM stack and a cloud tenant, with genuine adversary activity replayed in.

Browser-reachable

Open the range straight in your browser, no client, no install, available from any machine.

Safe by design

Segmented from any production network. Each team runs on its own instance and any host can be reset on demand.

Full telemetry

Host, network and cloud activity captured in full, so an attack and its evidence are visible at the same time.

Your range stays yours

You keep your own range for the whole track, repeat a lab, finish a challenge or practise whenever it suits you.

For teams & enterprises

Workforce capability you can actually measure.

The academy is built for individuals starting a career and for security leaders building one inside their organisation, with skill validated on evidence of real work, not attendance.

Career starters

Begin with no prior security knowledge and follow one deliberate line to a job-ready specialism, every hour spent operating a live enterprise, not watching slides.

SOC & security teams

Ramp analysts and responders on the same tooling and adversary activity they will face in production, and close known gaps with the track that maps to the role.

Security leaders

Give CISOs and team leads a defensible, evidence-based view of who can do the work, with team tracking, role-aligned paths and credentials mapped to recognised standards.

Business outcomes

What it changes for the organisation.

Faster ramp to productive

Structured, hands-on tracks shorten the path from hire to contributing on real work, on real tooling.

Skill validated on evidence

Graded capstones on the range certify what a person can actually do, not what a multiple-choice exam guessed.

Coverage across the team

One foundation feeds offensive, defensive, cloud and OT tracks, so capability scales across the whole function.

Mapped to recognised standards

HRC credentials align to industry certifications and MITRE ATT&CK, giving leaders a common language for capability.

Talk about team training Explore the range Team enrolment, role-aligned tracks and progress reporting.

Start at the foundation. Graduate job-ready.

Enrol on the range to begin Intro to Cyber, or talk to us about team training and the right specialist track for your people.