One suite. Proactive and reactive.
One interface to see everything across your organization and attack surface, and act on it. The Suite is agentic end to end: AI triages the alerts, shortens dwell time and speeds every step, with our experts governing every call.
The workspace where readiness lives.
Integrations, intelligence, endpoints, readiness and reporting, one shared workspace. These are the real screens.

Know how ready you are, before the bad day.
A scored readiness picture across your technology, your team and your documentation, with the exact gaps ranked and a plan to close them.
- One combined score a board can track quarter to quarter.
- Gaps ranked by impact, each with a concrete next step.
- Exportable as a PDF for auditors and insurers.

Eyes on every endpoint.
Deploy the HackersEye sensor in minutes, pick a policy, choose the platform, run one command. Every endpoint starts reporting to the SOC immediately.
- Windows, Linux and macOS, Intel and ARM.
- Policies set centrally; telemetry and detections follow.
- Fleet inventory shows every agent, live.

Know the threat before it lands.
Indicators and compromise data pulled from many sources and matched against your estate, updated constantly, and exportable to the tools you already run.
- Thousands of indicators across dozens of malware families.
- Sourced from real engagements, not a feed reseller.
- Push to MISP, STIX or your existing stack.

Proof, on demand.
A monthly SOC report and a library of 40+ ready-made reports mapped to HIPAA, ISO 27001 and SOC 2, generated from your live data in one click.
- Executive summary, incidents and trends, board-ready.
- Compliance packs mapped to the frameworks you answer to.
- Scheduled or one-click PDF, always from live data.
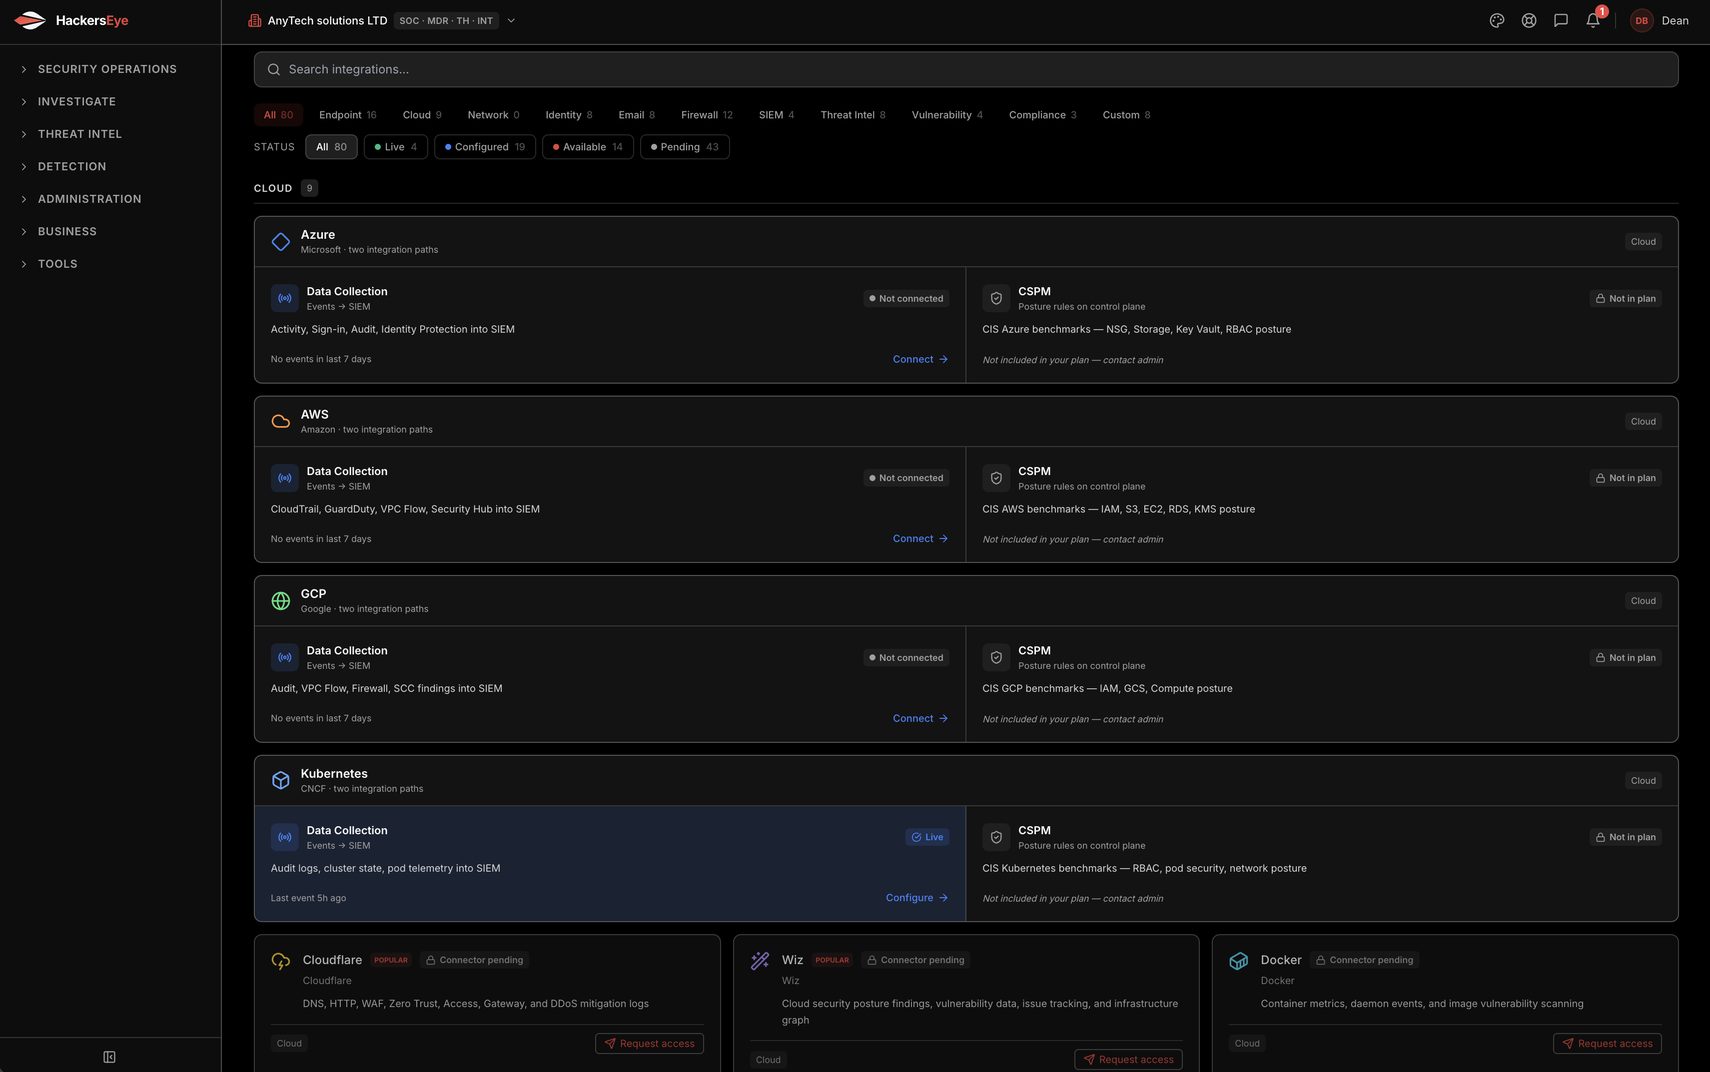
Every system, one screen.
Endpoints, cloud, email, identity and firewalls, all connected, all live, correlated into a single picture. See the whole organization and act on it from one place.
- All your telemetry, gathered and watched together.
- Posture scored against NIST, CIS and ATT&CK.
- AI triages the noise so the real threats surface fast.
Everything it takes, in one place.
From the telemetry you collect to the crisis you command, every module feeds one live picture, worked by AI and your team together.

SIEM
Every system on one screen, endpoints, cloud, email, firewalls and business apps, gathered and correlated as it happens.
EDR
Eyes on every server and workstation, so a threat surfaces the moment it moves on any machine.

CSPM
Your cloud watched and hardened, risky misconfigurations found and managed before anyone can use them.

Threat Intelligence
Indicators and compromise data from many sources, matched to your estate and updated constantly.

External Attack Surface
See yourself the way an attacker does, exposed assets and weak points float up to be fixed first.

Threat Hunting
Scheduled or on-demand deep hunts, you pick the type and scope, the Suite goes looking.
Supply Chain
Your vendors' risk is your risk, third-party exposure tracked across intel, attack surface and the assets they touch.
Crisis Command
A role-based war-room where everyone works one timeline, same facts, seen through each team's lens.

Executive Vault
One permission-based home for every report and deliverable, nothing missing, nothing exposed.

Sandbox
Detonate suspicious files safely and expose malicious behaviour before it reaches anyone.
AI carries the load. Our experts stay in command.
The Suite runs on AI agents that watch, correlate and triage across every module, around the clock, cutting response time, cost and blind spots. Nothing acts on its own: our team governs, validates and approves every step. The AI does the heavy lifting; our people stay accountable for the outcome.
Triage, automatically
AI ranks and filters the flood of alerts so the real threats rise to the top, and our analysts confirm each one before it moves.
Dwell time, cut
Threats are surfaced and correlated in seconds, not weeks, so our team can contain them long before they spread.
Always-on coverage
Agents watch every signal round the clock without tiring, and the SOC and MDR team reviews, validates and escalates what matters.
Sharper visibility
Signals from every module and source are correlated into one clear picture, so threats can't slip through the seams between tools.
Faster, consistent response
Routine response steps run instantly and identically, no missed step, no fatigue, each one reviewed and approved by an expert.
Continuously improving
Every incident sharpens the rules, models and detections, with our experts curating exactly what the system learns.
People stay in the loop, always. AI is powerful, but it's still young, so it never runs unchecked. Our experts monitor, validate and approve what the agents do and catch anything off before it ever reaches you. You get the speed of automation with the judgment and accountability of a team that runs real crises for a living, not a black box left to make its own decisions.
Built by the red teams who break in and the IR teams who run national-level breaches, the same attacker instinct and battle-tested judgment, poured into every module.
Thousands of rules and indicators, a holistic view of your whole estate, and a multidisciplinary way of working where every role sees the incident through its own lens.
- Proprietary detection rules, updated constantly from live incidents.
- Our own intelligence, leaked databases, fresh vulnerabilities, live indicators.
- IR, forensics and crisis playbooks, proven on national-level attacks.
Same incident. Different lens.
Role-scoped from one shared timeline, each seat sees exactly what it needs, and nothing it shouldn't.
The responder
Raw artifacts, IOC matches and process trees under chain-of-custody, triage in seconds, full image when the case earns it.
The commander
The whole picture on one timeline, who's doing what, the disclosure clock, the next decision the room owes the business.
Legal & comms
Legal hold, privileged channels and a defensible audit trail, plus the disclosure draft tracked against the clock.
The board
Quantified risk reduction and a narrative-grade pack, no raw IOCs, no jargon, just the number and the trend.
The Suite, fully operated.
Take the Suite and run it in-house, or have our team operate it for you around the clock. We can work over the Suite, over the tools you already own, or a mix of both.
24/7/365 SOC
Our analysts watch, triage and escalate around the clock, across the whole Suite, or just your SIEM. Nothing slips through overnight.
24/7/365 MDR
We watch your endpoints through the EDR, hunt the threats and contain them, on your machines, on our clock.
Respond
When the worst day comes, a named incident commander and our IR team are in the war-room with you, fast.
Delivered over our Suite, over your existing tools, or a combination, you choose what we run and what stays in your hands.
See the Suite in action.
Thirty minutes, live, with the team that runs it, you choose the modules, we show them working on real scenarios.